EdgeOne Hotlink Protection Practical Tutorial
Download
Focus Mode
Font Size
This document describes how to use the hotlink protection capability provided by EdgeOne to protect your content from unauthorized hotlink access and improve the security of your acceleration service.
Overview
Hotlinking refers to other websites or applications directly linking to your resources without your authorization. This behavior can severely impact your website. First, hotlinking consumes your bandwidth and server resources, causing your website to slow down or even crash. Second, hotlinking may lead to your content being misused or distributed without authorization, which can seriously damage your brand image and reputation.
To address these issues, EdgeOne provides a range of powerful hotlink protection capabilities. By using the hotlink protection feature of EdgeOne, you can ensure that only authorized users can access and use your content. You can configure an allowlist to permit only specific domains or IP addresses to access your resources, thereby blocking unauthorized hotlink access. Additionally, you can flexibly configure custom hotlink protection rules as needed.
With the hotlink protection capability of EdgeOne, you can effectively protect your content. You can confidently deliver high-quality content without worrying about hotlinking and abuse. This helps maintain your brand image and reputation while saving bandwidth and server resources and improving website performance and reliability.
Implementation Methods
HTTP response: Implements basic access control such as IP blocklist/allowlist, Referer blocklist/allowlist, User-Agent blocklist/allowlist, and regional access control. For details, see HTTP Response.The issues with this method are:
IP addresses can be forged or hidden, allowing attackers to bypass IP address allowlist and blocklist restrictions. They can use proxy servers, virtual private networks (VPNs), or other techniques to hide their real IP addresses and bypass access restrictions. This makes IP address allowlists and blocklists unreliable in preventing unauthorized access.
The Referer header is also easy to forge. Attackers can bypass Referer allowlist and blocklist restrictions by modifying the Referer field in HTTP request headers. They can use browser plugins, proxy tools, or other techniques to modify the Referer field so that it appears to come from a trusted source, thereby bypassing access restrictions.
The User-Agent header has similar issues to the Referer header and is also vulnerable to forgery.
Token authentication: Timestamp hotlink protection, which is more secure and reliable. For details, see Token Authentication.Compared to the basic access control mentioned above, its advantages and issues are as follows:
Prevent link reuse: each link contains a timestamp parameter. Even if a link is forwarded or shared, once the timestamp expires, others cannot use the link to obtain the resource.
Difficult to forge: timestamp-based hotlink protection increases the difficulty of hotlinking because attackers need to know the authentication algorithm, authentication key, timestamp format, and other information to construct a URL that passes validation, and this information is difficult for attackers to guess or forge.
Client-side modification is required: using this feature requires coordination between the client and EdgeOne. After the client initiates an encrypted URL request, EdgeOne validates the URL based on predefined rules. Therefore, additional overhead and complexity need to be considered during implementation.
Edge functions: Customizable hotlink protection capabilities such as remote authentication can be supported through Edge Functions.The advantages and issues of this method are as follows:
High security: remote authentication provides higher security. The authentication process is completed by a remote server provided by the customer rather than an EdgeOne node server, reducing the risk of theft by attackers.
Flexibility and scalability: remote authentication provides greater flexibility and scalability. Customers can flexibly control the authentication logic to adapt to changing business requirements and user access patterns.
Client-side modification is required: customers need to deploy a remote authentication service and ensure the reliability, security, and performance of the remote server to avoid increased authentication latency that affects service quality. In addition, an appropriate authentication timeout must be configured to handle potential exceptions. Typically, if authentication times out, the request is allowed directly. However, if the authentication service encounters an exception, unauthorized requests may be allowed, increasing security risks.
Operation Guide
Referer Hotlink Protection
Set access control rules based on the Referer field in HTTP request headers to identify and filter visitors, preventing website resources from being illegally stolen. Configure Referer allowlists and blocklists, and EdgeOne identifies request identities based on the lists to allow or deny access requests. If an access request is allowed, EdgeOne returns the resource link. If an access request is denied, EdgeOne returns a 403 response code.
Configuration Example
For your site
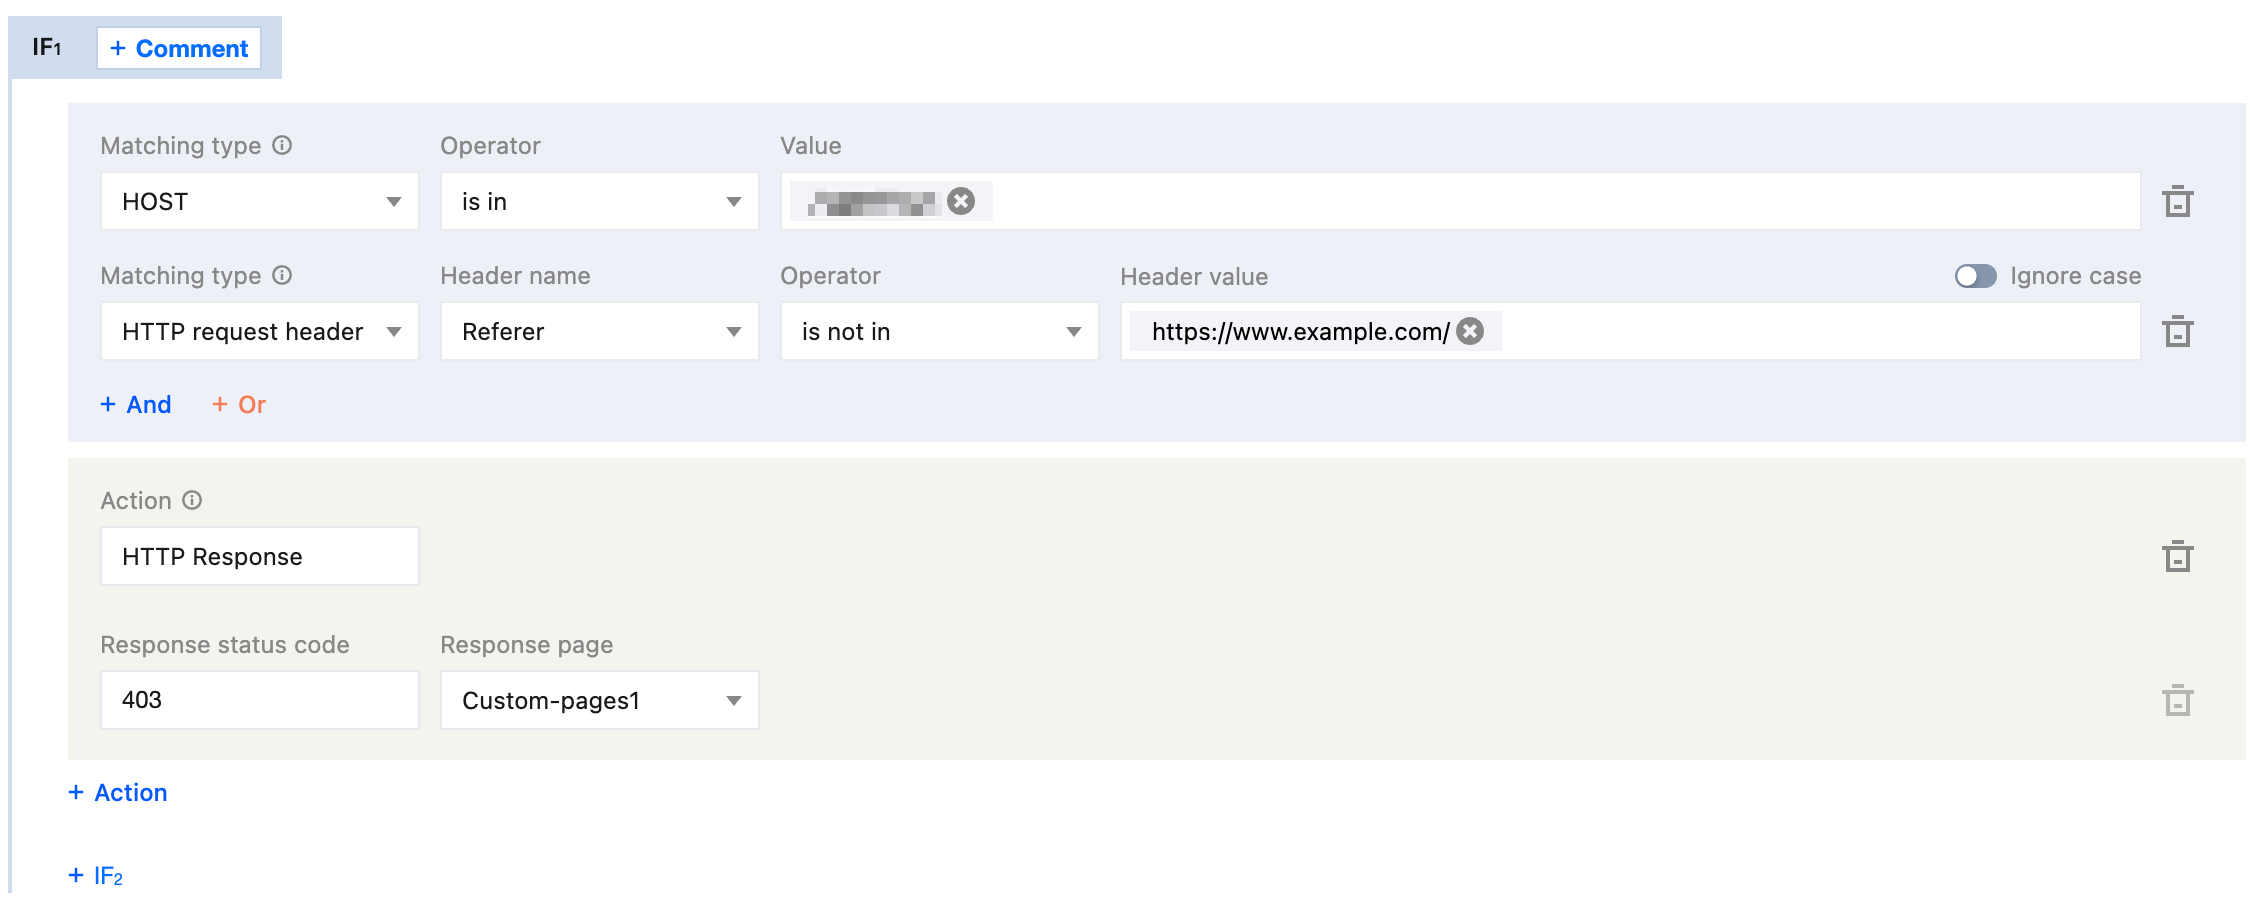
example.com, if you only allow access to the domain business www.example.com with the Referer set to https://www.example.com, and deny other requests directly with a 403 response, you can follow these steps:1. Log in to the EdgeOne console. In the left menu bar, go to Service Overview and click the site to be configured under SCDN.
2. On the site details page, click Site Acceleration to go to the site global configuration page, and then click the Rule Engine Tab.
3. On the Rule Engine page, click Create Rule and select Add Blank Rule.
3.1 On the rule editing page, set the matching type to HOST equal to
www.example.com, and set the matching type HTTP Request Header Referer's header value not equal to https://www.example.com/.3.2 Click Action, and in the pop-up operation list, select the operation as HTTP Response.
3.3 Configure the response status code as 403. Select the response page from the drop-down list. If no page is available, you need to click Create Page to create one first and then reference it.
4. The complete rule configuration is as demonstrated below. By clicking Save and publish, the rule configuration will be completed.
IP address blocklist/allowlist
By configuring IP address allowlists and blocklists to filter user requests and block or allow access from specific IP addresses, you can effectively restrict access sources and prevent issues such as malicious IP address-driven fraud and attacks.
Configuration Example
For your site
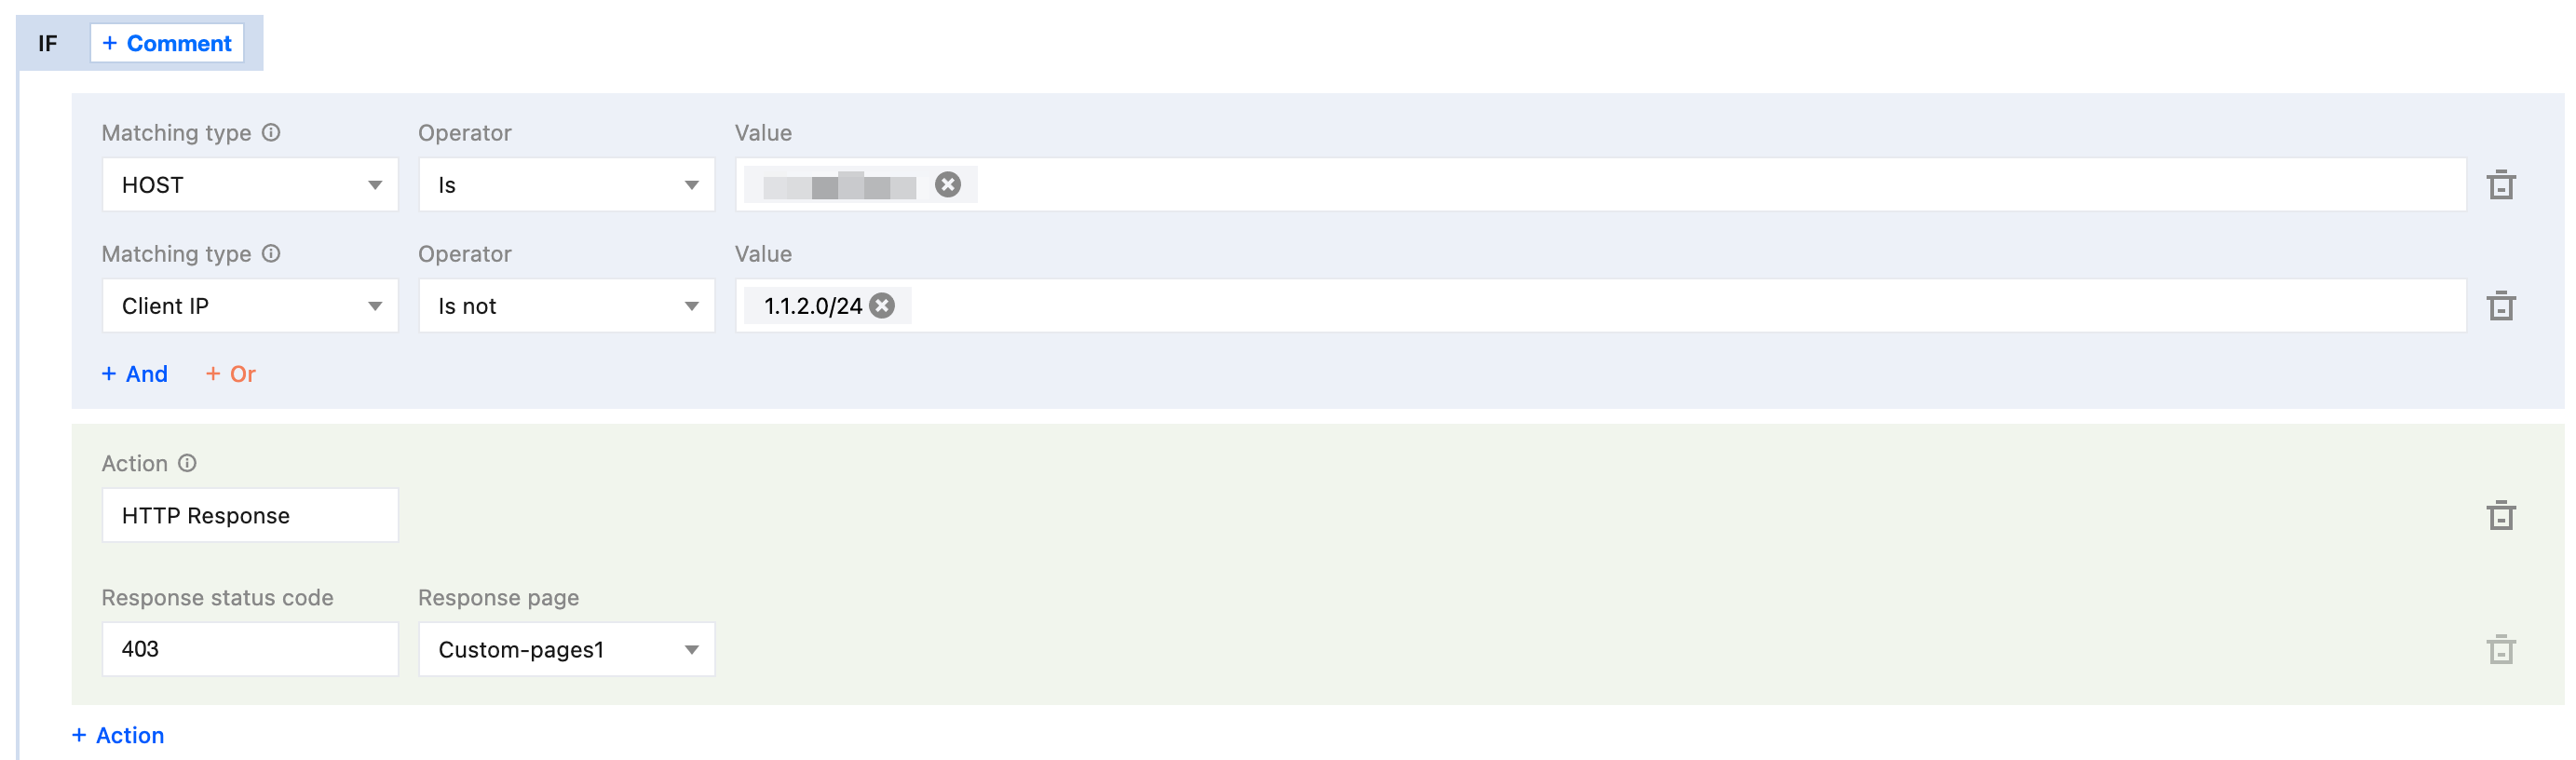
example.com, if you only allow access from client IP addresses within the range of 1.1.2.1 to 1.1.2.254 (including 1.1.2.1 and 1.1.2.254) to the domain business www.example.com, and deny other access directly with a 403 response, you can follow these steps:1. Log in to the EdgeOne console. In the left menu bar, go to Service Overview and click the site to be configured under SCDN.
2. On the site details page, click Site Acceleration to go to the site global configuration page, and then click the Rule Engine Tab.
3. On the Rule Engine page, click Create Rule and select Add Blank Rule.
3.1 On the rule editing page, set the matching type to HOST equal to
www.example.com, and set the matching type client IP Is not 1.1.2.0/24.3.2 Click Action, and in the pop-up operation list, select the operation as HTTP Response.
3.3 Configure the response status code as 403. Select the response page from the drop-down list. If no page is available, you need to click Create Page to create one first and then reference it.
4. The complete rule configuration is as demonstrated below. By clicking Save and publish, the rule configuration will be completed.
User-Agent Blocklist/Allowlist
The User-Agent is part of the HTTP request header and contains identifying information such as the operating system and version, browser type and version used by the user during access. You can configure User-Agent allowlist and blocklist rules to restrict the sources of users accessing your business resources, enhancing acceleration security.
Configuration example:
The domain business
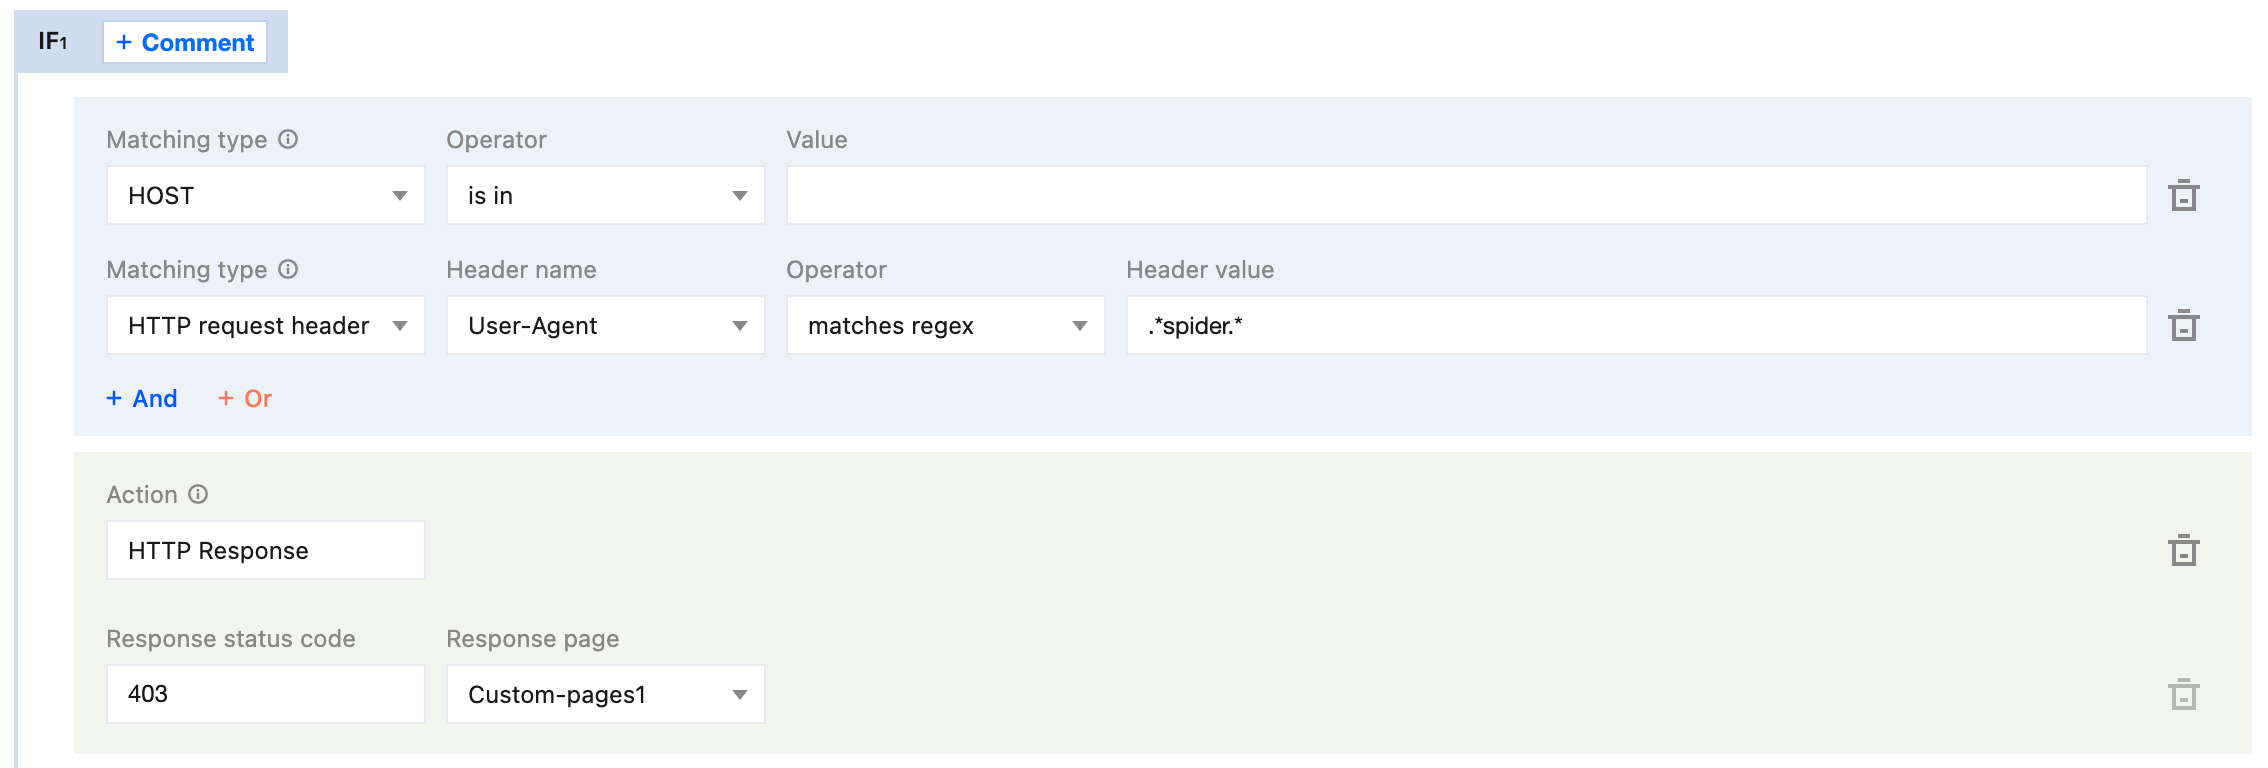
www.example.com under your example.com site is maliciously crawled by Google crawlers, causing a sudden bandwidth increase and severely impacting fees. Through analysis, it was found that the crawler request's User-Agent contains spider. If you want to block such requests, you can follow these steps:1. Log in to the EdgeOne console. In the left menu bar, click to go to Service Overview, and then click the site to be configured under SCDN.
2. On the site details page, click Site Acceleration to go to the site global configuration page, and then click the Rule Engine Tab.
3. On the Rule Engine page, click Create Rule and select Add Blank Rule.
3.1 On the rule editing page, set the matching type to HOST equal to
www.example.com.3.2 Click Action, and in the pop-up operation list, select the operation as HTTP Response, and set the matching type to HTTP Request Header User-Agent with a regular expression match for the header value
.*spider.*.3.3 Configure the response status code as 403. Select the response page from the drop-down list. If no page is available, you need to click Create Page to create one first and then reference it.
4. The complete rule configuration is as demonstrated below. By clicking Save and publish, the rule configuration will be completed.
Token Authentication
Token authentication is a simple and highly reliable access control policy. By configuring authentication rules for URL access validation, it can effectively prevent malicious hotlinking of site resources. The use of this feature requires cooperation between the client and EdgeOne. The client is responsible for initiating encrypted URL requests, and EdgeOne is responsible for legitimacy verification of the URL based on predefined rules. For detailed configuration and usage, refer to Token Authentication.
Remote Authentication
If you have your own authentication server, you can configure remote authentication to forward user requests to the authentication server you specify. The server then validates the requests. This method is suitable for scenarios requiring precise access control and real-time authentication. EdgeOne can achieve remote authentication capability through edge functions. For sample functions, refer to Remote Authentication.
Help and Support
Was this page helpful?
You can also Contact sales or Submit a Ticket for help.
Help us improve! Rate your documentation experience in 5 mins.
Feedback